Architecting for Active Containment: Lessons from the FBI Data Breach and the WebDesk Defense
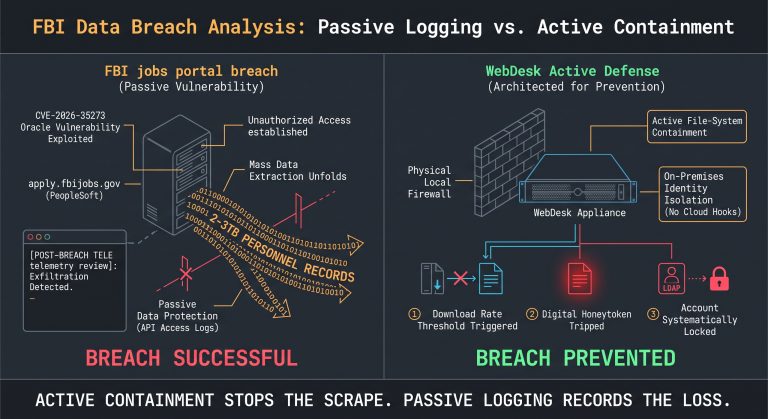
Executive Summary On September 22, 2026, the extortion group ShinyHunters claimed responsibility for a massive data breach targeting the FBI’s job application portal (apply.fbijobs.gov). The attackers bypassed a patch for an Oracle software vulnerability (CVE-2026-35273) on a public-facing web application,…